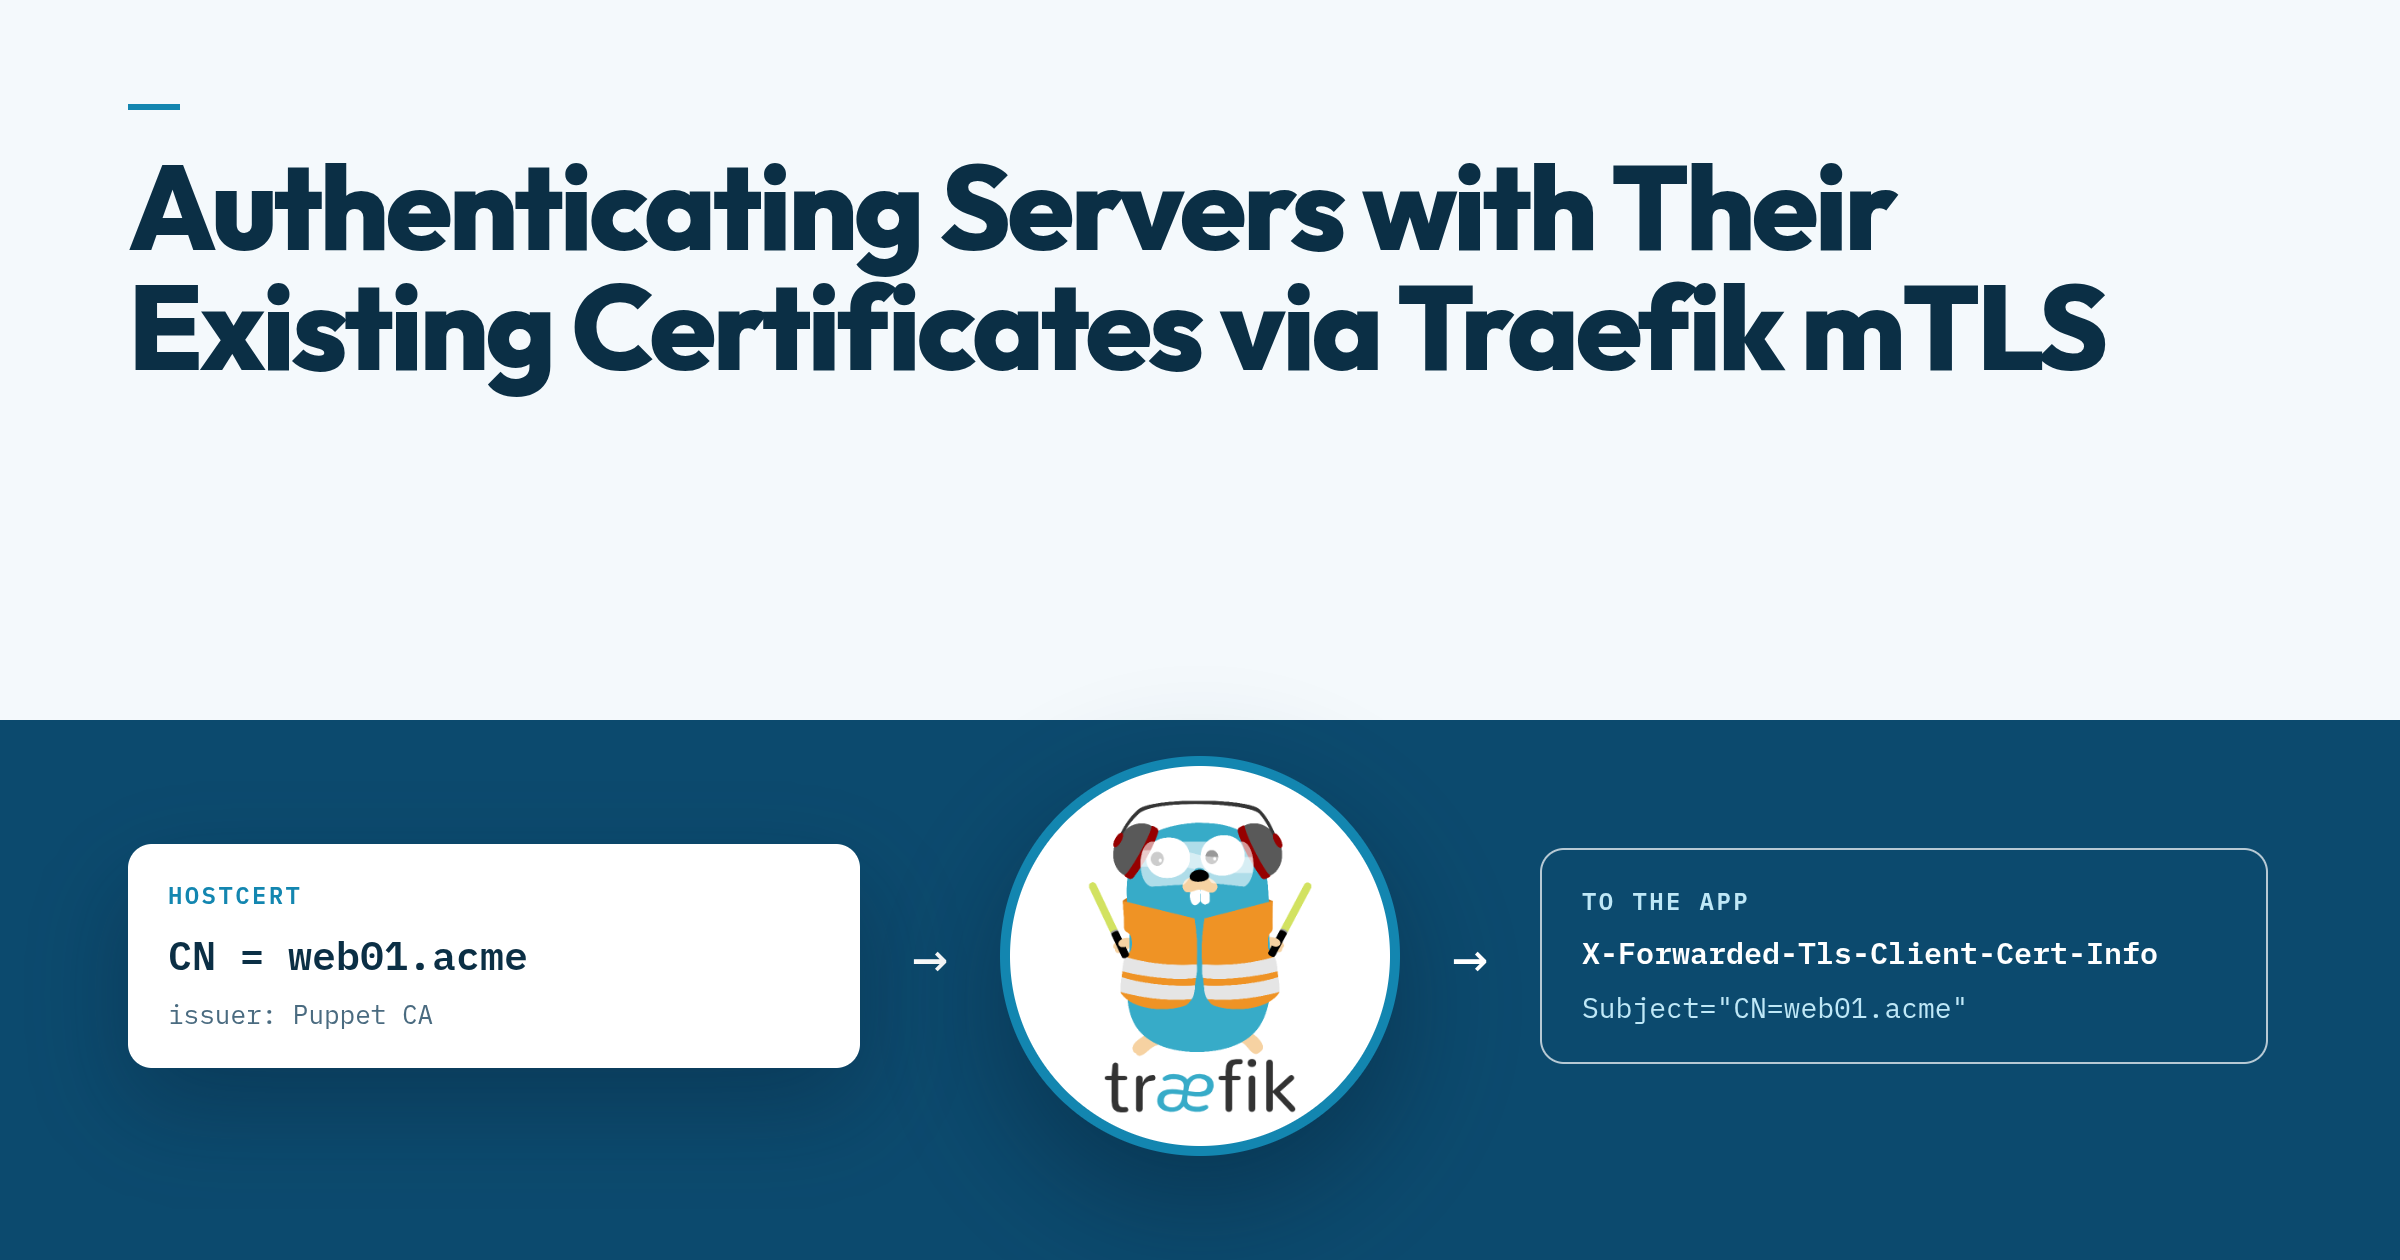
Authenticating Servers with Their Existing Certificates via Traefik mTLS
Why the servers I manage authenticate to services in Kubernetes with the certificate their Puppet agent already holds: the Traefik TLSOption and CA Secret, RequireAndVerifyClientCert versus VerifyClientCertIfGiven, the passTLSClientCert header the app reads, and the seven months a stale CA bundle rejected every server without anyone noticing.